Showing posts with label SECURITY NEWS. Show all posts

Monday, 26 September 2016

iPhone 7 owners fooled into drilling hole in their smartphones to ‘get a headphone jack’
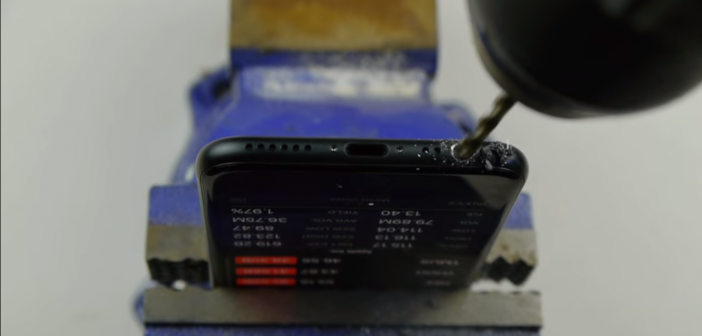

Clueless iPhone 7 owners destroy new handsets after YouTube prank tricks them into drilling their own headphone jack

A viral video from TechRax has been creating a lot of problems for iPhone 7 users. The fake video which purports to be a DIY for adding a 3.5mm headphone jack to the jackless iPhone 7 is actually causing iPhone 7 users to drill an actual hole in their new and shining iPhone 7 in search of the elusive 3.5 mm headphone jack.
When Apple officially announced its iPhone 7 without the traditional 3.5mm headphone jack, the decision irked a lot of Apple fans. The reason behind the removal of headphone jack technology in favour of Bluetooth headphones was to make more room for internal hardware.
However, a YouTube video has been doing the rounds of the internet, promoting a fake iPhone DIY hack that promises to “restore your headphone jack.” The video’s description reads, “This video is for those who don’t want to get $159 wireless AirPods or have to insert your headphones into an adapter every time you listen to music.”
The video advises iPhone users to clamp their precious new mobiles in a place where the headphones used to get inserted before creating their own jack with a 3.5mm drill to create a hole. The man in the video proudly declares, “And just like that, you have your own 3.5 mm headphone jack!”
Many iPhone 7 owners tried doing this by utilising 3.5mm drills as the video recommended ended up with damaged smartphones.
iPhone 7 drill
One user commented on the video, “I’ve just done this but there is no sound coming from the headphones. I used an exact 3.5mm drill bit but the connector doesn’t sit flush in the hole for some reason. The phone doesn’t even detect the headphones are in. Are there any settings I need to change?”
Furious James Ceja commented on the video: “I tried this and ended up with display destruction and it not working… I really committed the biggest mistake of my life by watching this video.”
David Iriarte added: “A friend of mine told me it worked for him, but my iPhone won’t turn on after I drilled the hole for the jack.
“I checked and it was the 3.5mm drill, so I made no mistake there! What happened? Any of you have the same problem?”
Toekneechair questioned: “Ok I am sure it’s in the comments somewhere but my friend told me to ask what size drill bit am I supposed to use?
“Also I don’t have that clamp thingy, can I or my friend hold it while we drill? I don’t want to ruin my phone.
“Thanks for all the help guys…”
Several users took to the YouTube video’s comment box to voice their displeasure. The video has since gone viral and more unsuspecting people are getting fooled to do the same.
Watch the below DIY video in action. WARNING: Please do not use a drill on your iPhone.
This isn’t the first time that smartphone owners are falling for fake hacks that could potentially brick their smartphones. In Pakistan, smartphone users fell for a fake video saying that Samsung smartphones have a chip embedded in batteries which spies on them. Hundreds of Pakistanis destroyed their smartphone batteries and NFC chips in search of the elusive chip.
Falling for fake hacks which could brick their smartphones isn’t restricted to Android smartphone owners, iPhone owners have also been duped similarly by fake hacks. Remember the video that went viral and promised iPhone users “recharge” their iPhones simply by putting it in a microwave? Another one tricked iPhone users into believing that iOS7 would make their phones waterproof!
Source: TechWorm

Friday, 23 September 2016

Logitech Harmony Home Control


Do yourself a favor and throw your basic $4 universal remote in the garbage can — that’s not a man-approved remote control, sorry. And, let’s face it, you lose it all too often anyway. One cool gadget you need in your life is a Logitech Harmony Home Control, a universal smart remote and base that allows you to use your smartphone as a remote as well. The device not only works with the majority of your entertainment devices, but also your home automation devices like Philips Hue or Nest Learning Thermostat (so you can lower the lights or change the temperature without even leaving your seat). The Logitech Harmony Home control works with over 270,000 devices, including TVs, satellite and cable boxes, blu-ray players, Apple TV, Roku, Sonos, Xbox, Philips Hue and more. So if you want to control the world around you without having to get up, pick up the Logitech Harmony Home Control — you’ll feel like a wizard!
Price: $149.99
Source: Heavy Gadgets

Divoom Voombox


Hey, guess what? It’s summertime! It’s time to be outdoors! And one of the cool gadgets that are necessary for the outdoorsy type of man is the Divoom Voombox Portable Wireless Speaker. The speaker connects to your devices effortlessly through Bluetooth, and the quality is absolutely astonishing. The Voombox blows many of the other wireless speakers out of the water when it comes to audio quality, especially the Westinghouse Unplug speaker that I’ve been recommending to everyone. The Voombox has a lot of boom for your buck, is water resistant, and is an especially great summer gadget for impromptu jam sessions, beach days, while you’re working on the car in the garage, or deck parties.
Price: $79.90 (20 percent off MSRP)
Soource: Gadgets 2016

LightMate Emergency LED Flash Light


The Satechi LightMate Emergency LED Flash Light is much more than just a flash light. In fact, Satechi’s only mistake with this flash light is that they didn’t name it something like the Smart Light. This cool gadget has a ton of practical applications. First and foremost, of course, it has a super-bright LED light that’s safe (plastic), long lasting and highly visible. The light has 5 different modes, including bright, medium, dim, SOS and strobe. Secondly, it contains a 2200mAh portable power bank with a USB charging port and cable for emergency cell phone charging. It’s also waterproof and highly durable, with a nice weight to it. Finally, it also has a high-strength pointed alloy steel emergency glassbreaker in case you ever need it. The only situation I can imagine needing it is during a zombie apocalypse and you’re trying to break glass to grab an axe. At least, that’s the scenario I have worked out in my head. Still, the LightMate Emergency Flash Light makes a great gift for campers, travelers or anyone that frequently uses a flash light.
Price: $29.99
Source : http://heavy.com/

Thursday, 22 September 2016

Do you cover your webcam? Privacy is important


Privacy is important. If your webcam gets hijacked, hackers can record you with your notice. It’s good to cover your webcam with small sticker on it to stop the CIA reading your brainwaves.


Hackers are really interested in spying upon others and steal information. They like to record a video footage about you from your computer without your permission and blackmail you for money or something else.

Make sure you run up-to data anti-virus software that help’s you to detect any malware in your computer.


If you are looking for some good webcam covers then check out this link from amazon.com.

Yahoo expected to confirm data breach affecting 200 million users: Report


Yahoo to go public about massive data breach affecting its 200 million users

Yahoo! Inc., is expected to officially acknowledge the massive data breach that took place last month with more than 200 million of users account exposed to hackers, Recode reports. While there is no confirmed information about the extent of the breach yet, the sources say that it is “widespread and serious” with the possibility of legal action and investigations led by the government.
Back in August, it was reported by Motherboard that a hacker going by the name of ‘Peace’ claimed to have breached Yahoo and put the usernames and passwords for over 200 million accounts up for sale. The same hacker has previously sold large data dumps of breaches related to Myspace and LinkedIn on a dark web marketplace called the Real Deal. The data dump allegedly included usernames, encrypted passwords, birthdays and other email addresses from 2012.
“It’s as bad as that,” one source told Recode. “Worse, really.”
The data was being sold for 3 bitcoins, worth $1,860 at the time. The company never issued password resets, a usual course of action taken by websites that would indicate of a hack. At the time, the company’s response to the hack was only that it was “aware of [the]claim” but did not confirm or deny that Yahoo users were affected.
The company said in a statement at the time, “We are committed to protecting the security of our users’ information and we take any such claim very seriously. Our security team is working to determine the facts.”
This news comes at a time when Yahoo is the middle of a mega-acquisition by Verizon in a $4.8 billion deal, which is yet to be approved by regulators and shareholders. So, it would be interesting to see if the deal would face repercussions due to the breach.
Yahoo is rumoured to make its announcement this week. If Yahoo confirms the news, this would become the biggest hack of its kind in the Yahoo history. If you own a Yahoo account, it would be ideal to change your password as soon as possible. Also, if you’re using the same Yahoo username and password combination elsewhere, it is recommended to change those as well.
Source : Techworm

Go Get a Replacement For Your Exploding Samsung Note 7


Replacements are now available for Samsung's recalled, exploding phone.


Samsung says new Galaxy Note 7 smartphones will be available in U.S. stores starting Wednesday to replace about 1 million devices that are being recalled because their batteries can catch fire.

The South Korean company has been scrambling to fix problems caused by faulty batteries in the latest version of its top-of-the-line smartphone, which first went on sale last month.

When it first offered on Sept. 2 to replace the affected Note 7 phones, Samsung said it would swap them for models of its other phones, such as the Galaxy S7, until supplies of replacement Note 7 devices became available.

Samsung followed up last week by announcing that U.S. consumers who had purchased one of the recalled phones could choose between a replacement or a refund for the device, which sells for about $850. That offer wasjointly announced with officials at the U.S. Consumer Product Safety Commission after Samsung was criticized for not coordinating more closely with the commission.

Safety officials have urged Note 7 owners to turn off their phones and return them immediately. They cited reports of Note 7 batteries overheating in the United States, including 26 instances where individuals were burned and 55 that caused property damage.

The problem doesn't affect all Note 7 phones, because Samsung uses batteries from different suppliers. But the company has said about 2.5 million devices may be affected worldwide, including 1 million sold in the United States.

Samsung also said it's pushing out two software updates through wireless carriers. One will show a green battery icon to confirm that a Note 7 device is a new one that doesn't have the battery problem. The other will display a short notice to owners of older phones covered by the recall, telling them to turn off their device and take it in for a replacement.

About a quarter of affected phones had been exchanged in the United States by Tuesday, according to a spokeswoman for Samsung's U.S. subsidiary. She was unable to say how many Note 7 buyers sought refunds, but said "the vast majority" received a different Samsung phone as a replacement.

Wednesday, 20 July 2016

40 Million iCloud Accounts Hacked? Hackers Hold iOS Devices To Ransom


Massive 40 Million iCloud Accounts Hack Could Hold Apple Devices Hostage For Russian Ransomware

Apple’s iCloud account appears to have been so severely hacked by some urbane hackers that some iPhones have essentially been held hostage for Russian ransomware. It is guessed that an astounding 40 million iCloud accounts (approximately) are rumoured to be at risk, according to CSO Online.
Some iPhone users, dating back to February this year, have discovered that their devices have been compromised, and are held hostage by Russian hackers. The attack is almost too simple.
An iCloud account is broken into (with the help of leaked credentials), and the service’s “Find My iPhone” feature.
“It starts with a compromised Apple ID. From there, the attacker uses Find My iPhone and places the victim’s device into lost mode. At this point, they can lock the device, post a message to the lock screen and trigger a sound to play, drawing attention to it.
In each of the cases reported publicly, the ransom demanded is usually $30 to $50. If a victim contacts the referenced email address, in addition to payment instructions, they’re told they have 12 hours to comply or their data will be deleted,” said CSO security blog Salted Hash.
If a slew of iCloud accounts are breached, you can multiply that $30 – $50 by 1,000 or even more, and the scheme suddenly looks rather lucrative to the hackers.
Earlier this week, a security professional posted a message to a private email group requesting information related to possible compromise of at least 40 million iCloud accounts.
Salted Hash started excavating on this story after the email was received. In it, a list member questioned the others about a rumour concerning “rumblings of a massive (40 million) data breach at Apple.”
The message goes on to state that the alleged breach was carried out by a Russian actor and vector “seems to be via iCloud to the ‘locate device’ feature, and is then locking the device and asking for money.”
The report adds that “for now, let’s assume there hasn’t been a massive iCloud data breach.” Apple has not commented on the matter.
Given that the Apple ID credentials involved in the ransom attacks are believed to originate from online security breaches, Salted Hash pointed towards a recently compromised Mac-Forums.com database, which allegedly includes 291,214 accounts, being sold for around $775 on the darknet.
However, some security experts are claiming that the victim count of 40 million is likely way overblown. It does make sense, because even if only a small percentage of the list were being attacked, a few hundred thousand victims within a few months would standout like a beacon. In short, there would be no way to keep such attacks under the radar. That’s not a glitch that would escape Apple’s radar, as you can imagine.
At this point of time, there is no evidence to suggest that the Mac-Forums database has any relation to these ransom attacks. However, if you wish to tread caution, it is highly recommended that you immediately change your iCloud password, and if you haven’t already, enable two-step verification. Both these changes can be done inside of your iCloud Settings screen.
Source: CSO Online

Sunday, 17 July 2016

Top 10 vulnerability scanners for hackers and researchers


Top 10 vulnerability scanners for hackers to find flaws, holes and bugs

Hacking is an art of finding bugs and flaws in a perfect software which will allow cyber criminals to exploit it for their own malicious gains. Hackers are mostly able to spot the flaws and bugs on their own but sometimes it is worthwhile to use a automated software to find these bugs and holes. A vulnerability scanner is such a automated software which has specifically been written to find such flaw.
Vulnerability Scanner is a specialised software build with a sole purpose of helping security researchers, hackers, system admins and developers to find faults in a particular software, computer system, network and servers. A hacker or security researcher is complemented in his manual testing of software or computer by using such vulnerability scanner making the hackers assessment efficient.
This article brings out such top 10 vulnerability scanner tools available to help hackers and security researchers in their security testing mission.

OpenVAS

The Open Vulnerability Assessment System (OpenVAS) is a framework of several services and tools offering a comprehensive and powerful vulnerability scanning and vulnerability management solution.  The actual security scanner is accompanied with a daily updated feed of Network Vulnerability Tests (NVTs), over 33,000 in total (as of December 2013).
All OpenVAS products are Free Software. Most components are licensed under the GNU General Public License (GNU GPL). The OpenVAS is available for FREE and for Linux, Windows and other operating systems.

MBSA

The Microsoft Baseline Security Analyzer provides a streamlined method to identify missing security updates and common security misconfigurations. MBSA 2.3 release adds support for Windows 8.1, Windows 8, Windows Server 2012 R2, and Windows Server 2012. Windows 2000 will no longer be supported with this release.
MBSA is a FREEWARE and is available only for Windows operating system.

Secunia PSI

Don’t let one vulnerable PC open your corporate network up to cyber attacks – Combining private and corporate Patch Management provides a 360° overview of all vulnerability threats.
The Secunia Personal Software Inspector (PSI) is a free security tool designed to detect vulnerable and out-dated programs and plug-ins, which expose your PC to attacks. Once installed, the Secunia PSI can help you patch vulnerable programs and stay secure.
Secunia PSI is available for free and works only with Windows operating system

Nipper

Nipper (short for Network Infrastructure Parser, previously known as Cisco Parse) audits the security of network devices such as switches, routers, and firewalls. It works by parsing and analyzing device configuration file which the Nipper user must supply. This was an open source tool until its developer (Titania) released a commercial version and tried to hide their old GPL releases (including the GPLv2 version 0.10 source tarball).
Nipper is available for Windows, Apple MAC OSX, Linux and is a PAID software.

Retina

With over 10,000 deployments since 1998, Beyond Trust Retina Network Security Scanner is the most sophisticated vulnerability assessment solution on the market. Available as a standalone application or as part of the Retina CS unified vulnerability management platform.
Retina Security Scanner enables you to efficiently identify IT exposures and prioritize remediation enterprise-wide. Retina Network Security Scanner, the industry’s most mature and effective vulnerability scanning technology, identifies the vulnerabilities – missing patches, configuration weaknesses, and industry best practices – to protect an organization’s IT assets.
Retina is a PAID vulnerability scanner tool and only available for Windows operating system.

Nexpose

Nexpose, the vulnerability management software, proactively scans your environment for mis-configurations, vulnerabilities, and malware and provides guidance for mitigating risks. Experience the power of Nexpose vulnerability management solutions by knowing the security risk of your entire IT environment including networks, operating systems, web applications, databases, and virtualization.
Exposing security threats including vulnerabilities, mis-configurations and malware.
Prioritizing threats and getting specific remediation guidance for each issue. Integrating with Metasploit to validate security risk in your environment.
Nexpose is available for Windows and Linux operating systems and is a paid software.

GFI Lan Guard

Research consistently demonstrates that many of the vulnerabilities cybercriminals exploit can be prevented with updated software patches, and addressing of misconfigured network gear and unauthorized devices on the network.
GFI LanGuard scans and detects network vulnerabilities before they are exposed, reducing the time required to patch machines on your network. GFI LanGuard patches Microsoft ®, Mac® OS X®, Linux® and more than 50 third-party operating systems and applications, and deploys both security and non-security patches.
GFI Lan Guard is a paid software and only works on Windows operating.

Core Impact

As network security continues to harden, it’s no surprise that cyber criminals have shifted their attack techniques to focus on applications and end users.
With the release of version 12.5, CORE Impact Pro takes vulnerability assessment and testing far beyond traditional exploitation — allowing commercial and government organizations to actively and accurately test the security of their network and application infrastructure using the same Advanced Persistent Threat and password-based techniques employed by cyber attackers.
Core Impact is a paid software is available for Windows operating system.

QualysGuard

QualysGuard Enterprise is an award-winning cloud security and compliance solution. It helps global businesses simplify IT security operations and lower the cost of compliance. It delivers critical security intelligence on demand and automates the full spectrum of auditing, compliance and protection for Internet perimeter systems, internal networks, and web applications.
QualysGuard is a paid software and only works with Windows operating system.

Nessus

The Nessus vulnerability scanner provides patch, configuration, and compliance auditing; mobile, malware, and botnet discovery; sensitive data identification and many other features.
  • Nessus and Nessus Perimeter Service™ subscriptions for commercial organizations and enterprises
  • Nessus evaluations for commercial organizations
  • Nessus Home for personal use in a non-commercial, home network
Nessus is a multi platform PAID software and works with Windows, Mac OS X, OpenBSD, FreeBSD, Solaris, and/or other UNIX variants.

Source http://www.techworm.net/2016/07/top-10-vulnerability-scanners-hackers-researchers.html